Lunduke
News • Science & Tech
Tea App Clone Exposes Driver’s Licenses
Last month the Tea App exposed 60 GB of personal data (including the government ID of users). Now a clone "TeaOnHer" App did the exact same thing. The future is stupid.
August 13, 2025
post photo preview

Last month, we saw the massive data breach of the “Tea App” — a smartphone app for women to talk about men they don’t like — resulting in over 60 GB of personally identifiable data leaked out to the public. Stuff like selfies and pictures of drivers licenses.

Well, it didn’t take long for a “TeaOnHer” App to appear — with the same basic functionality, except this time for men to talk about women they don’t like.
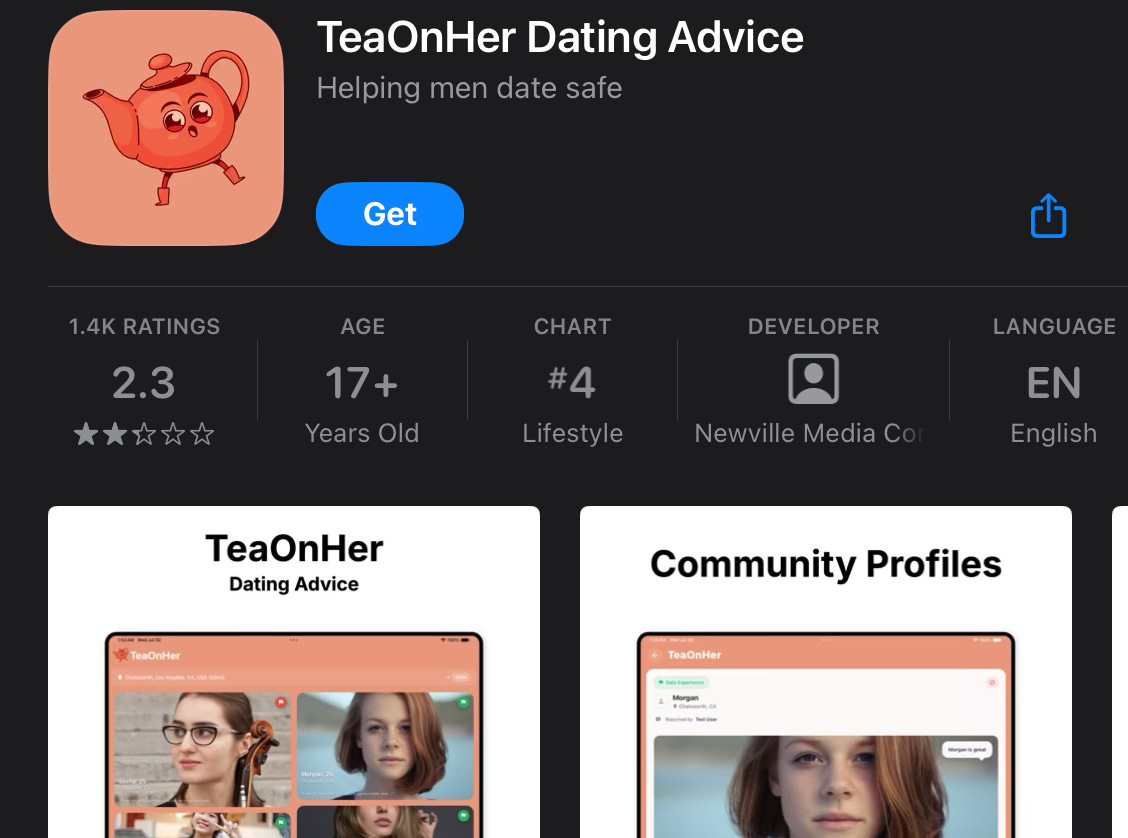
 

And, of course, the developer of “TeaOnHer” made the same basic mistake that the “Tea App” made: They permanently stored a ton of personal information. Including, once again, divers licenses.

You can already see where this is going.

Driver’s Licenses Everywhere

Almost as soon as the “TeaOnHer” app went live, writers for TechCrunch went looking to see if they could easily access any of that data. Because wouldn’t that be crazy if a copy-cat app made the exact same kind of security mistakes as the app it was copying?

What TechCrunch found was that it took no more than around 10 minutes for them to begin accessing pictures of drivers licenses of user accounts.
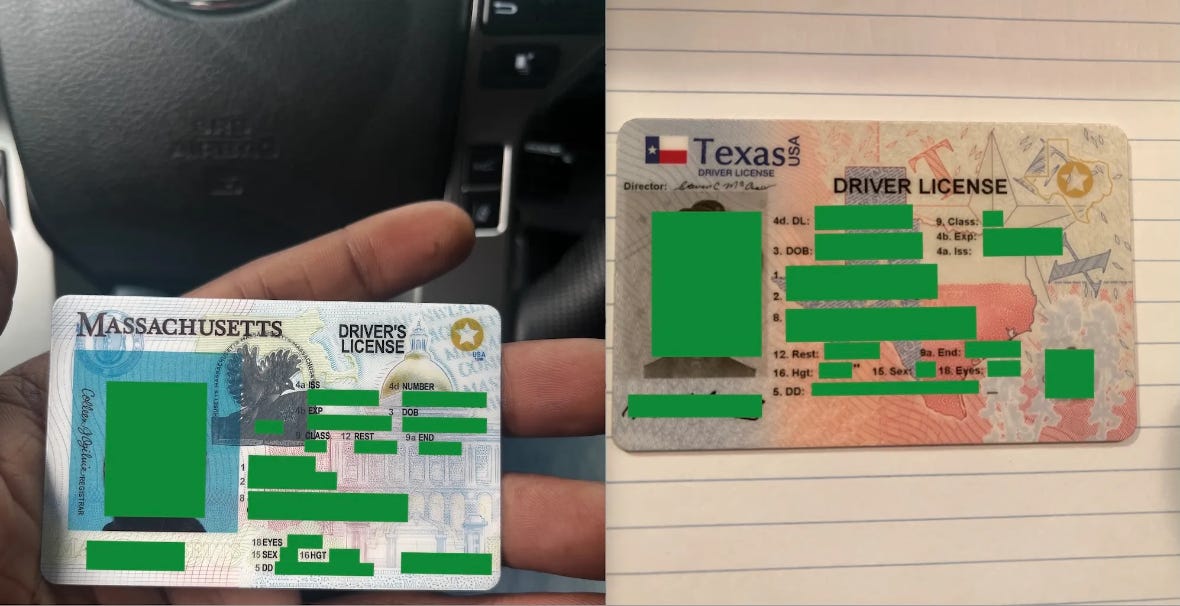
 

10 minutes!

With a bunch of the usual suspects of bad security being involved: unprotected file storage (in this case, Amazon), public API documentation, and a lack of secured API calls.

Now, unlike the “Tea App” breach — which resulted in massive archives of personal data published all over the web — it isn’t known if these vulnerabilities actually resulted in significant data archives getting out there in the wild.

But, as the writers at TechCrunch put it, “The bugs were so easy to find that it would be sheer luck if nobody malicious found them before we did.”

There’s a Lesson Here… But it Won’t Be Learned

Sure, this “hack” of the “TeaOnHer” App was easy — as was the hack of the “TeaApp” before it. Both of those systems were comically insecure.

But, the reality is, no complex online system is truly secure.

Have a website or App which stores (and publishes) user data? It can be hacked.

And, if there is sufficient interest in obtaining whatever data is being stored, not only can it be hacked… but it will be hacked.

The HaveIBeenPwned site, alone, has documented close to 15 Billion (with a B) accounts which have not only been breached… but reported and (often) made available in some way.
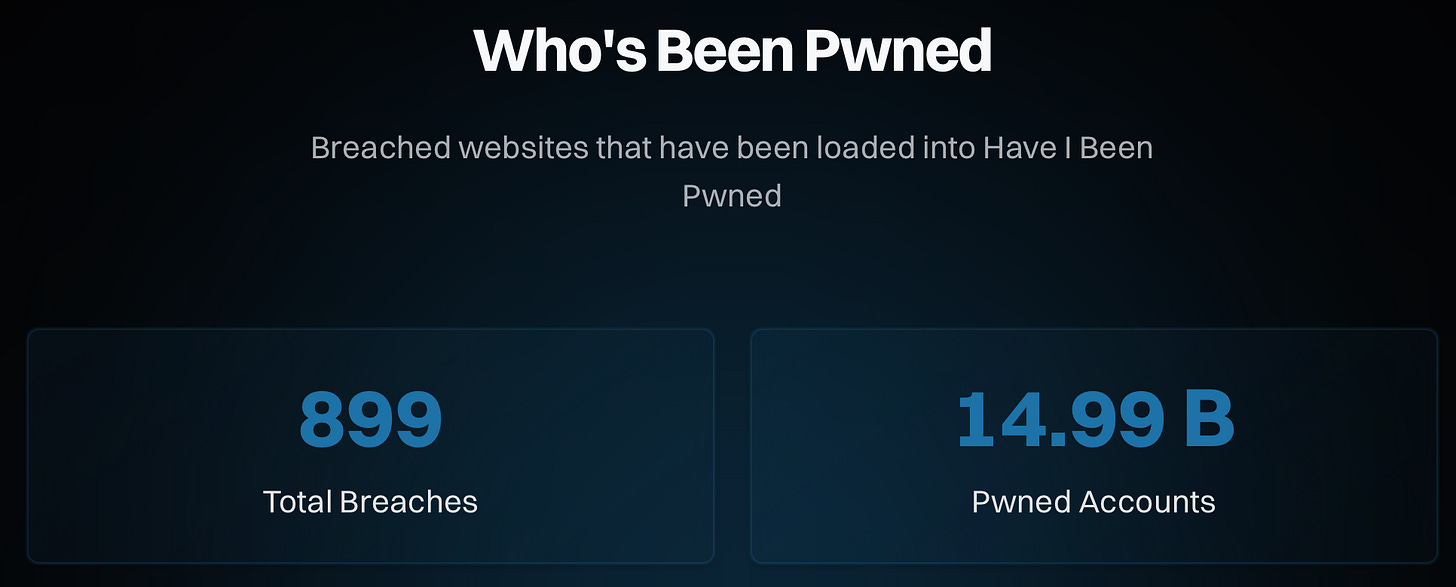
 

And that 15 Billion is only the breached accounts which we know about.

Anyone who works in IT can tell you that the vast majority of data breaches are never discovered. And the majority of those which are discovered… are never disclosed publicly.

Considering that the current population of the Earth is roughly 8 Billion, it’s safe to assume that every single adult on Earth, with an Internet connection, probably has several breached accounts already.

With the frequency, and size, of such data breaches increasing.

Should these Tea Apps have had better security? You bet your tuchus. From the looks of things neither developer spent any significant time trying to implement even the most basic security precautions.

For Pete’s sake, at least try to slow the hackers down a little.

But the real problem here is not the total lack of security — even “good” security can (and will) be overcome.

No.

The real problem is the type of data being permanently stored, in an Internet accessible way, by these services. If a service is likely to be breached (and any significant service is), a key goal is to limit the amount of data which a hacker can gain access to.

Here are a few good rules of thumb when dealing with data being stored on an Internet accessible server:

  • Do not store any more data, at any given moment, than is 100% necessary.

  • If previously stored data is no longer needed, delete it. Completely. Not “flagged” for deletion. Actually deleted.

  • Whatever data you are storing should be encrypted whenever possible.

  • If sensitive personal data absolutely must be stored, for legal and regulatory reasons, consider physical archives stored in a secure location instead of an Internet connected server.

  • And, of course, don’t use unprotected (or barely protected) “cloud” file storage like the numbskull developers of these “Tea” apps did. That never ends well.

Simple guidelines which, if followed, could significantly reduce the negative impact of inevitable data breaches.

But, of course, few online services — big or small — will follow such guidelines. They will continue expanding the quantity of data they store on increasingly complex systems.

Which means we’ll see more and more data breaches — containing an ever increasing amount of personal data.

Welcome to the future.

The stupid, stupid future.

community logo
Join the Lunduke Community
To read more articles like this, sign up and join my community today
5
What else you may like…
Videos
Podcasts
Posts
Articles
November 04, 2026
"No one is seriously considering" Rust Clones says Fedora Developer

"Deliberate breakages and incoherent incompatibilities make [Rust CoreUtils Clones] a non-starter... We're probably not ever going to switch to it in Fedora."

The Lunduke Journal & LCOS:
https://lunduke.com/

00:07:53
November 03, 2026
Everyone Loves LCOS... Except Leftists

Early reviews for the Lunduke Computer Operating System 1.0 range from "Amazing" and "Perfect"... to "Nazi" and "Not even if he paid me".

LCOS on DistroWatch:
https://distrowatch.com/table.php?distribution=lcos

The Lunduke Journal & LCOS:
https://lunduke.com/

00:11:39
November 02, 2026
Firefox Asks "Who Destroyed Privacy?" After Waging Years Long War on Privacy

Mozilla does the "fall off the bicycle" meme after years of working to destroy online privacy.

The Lunduke Journal & LCOS:
https://lunduke.com/

00:07:00
November 22, 2023
The futility of Ad-Blockers

Ads are filling the entirety of the Web -- websites, podcasts, YouTube videos, etc. -- at an increasing rate. Prices for those ad placements are plummeting. Consumers are desperate to use ad-blockers to make the web palatable. Google (and others) are desperate to break and block ad-blockers. All of which results in... more ads and lower pay for creators.

It's a fascinatingly annoying cycle. And there's only one viable way out of it.

Looking for the Podcast RSS feed or other links? Check here:
https://lunduke.locals.com/post/4619051/lunduke-journal-link-central-tm

Give the gift of The Lunduke Journal:
https://lunduke.locals.com/post/4898317/give-the-gift-of-the-lunduke-journal

The futility of Ad-Blockers
November 21, 2023
openSUSE says "No Lunduke allowed!"

Those in power with openSUSE make it clear they will not allow me anywhere near anything related to the openSUSE project. Ever. For any reason.

Well, that settles that, then! Guess I won't be contributing to openSUSE! 🤣

Looking for the Podcast RSS feed or other links?
https://lunduke.locals.com/post/4619051/lunduke-journal-link-central-tm

Give the gift of The Lunduke Journal:
https://lunduke.locals.com/post/4898317/give-the-gift-of-the-lunduke-journal

openSUSE says "No Lunduke allowed!"
September 13, 2023
"Andreas Kling creator of Serenity OS & Ladybird Web Browser" - Lunduke’s Big Tech Show - September 13th, 2023 - Ep 044

This episode is free for all to enjoy and share.

Be sure to subscribe here at Lunduke.Locals.com to get all shows & articles (including interviews with other amazing nerds).

"Andreas Kling creator of Serenity OS & Ladybird Web Browser" - Lunduke’s Big Tech Show - September 13th, 2023 - Ep 044
15 hours ago
9 hours ago

SSD vs HDD: The Ugly Truth Nobody Wants to Admit - YouTube

November 05, 2026

The unemployment will be given a nice 6 week abatement!

I start a 6 week assessment engagement starting November 16th. 5 months - second longest time of unemployment.

The field seemed dead from mid July until a couple weeks ago. I have several irons in the fire at the moment.

Still, it was a just-in-time opportunity as companies close down hiring during the holidays and typically through January.

Did AI take away all the jobs? I can't say that. There are ebs and flows I've experienced before and this didn't feel different.

Were a LOT of the job opportunities about AI? Yes. I would have been more worried had I not been investing in developing AI skills the past 3 years.

Did the job I land involve AI? No. Will I use AI? To prep before-hand? Absolutely. I'm thrilled at what I'm putting together so that I can show up day one and rock this assignment.

I don't think the client is using AI so I don't think I'll be allowed to. Six weeks - that's fine with me.

October 28, 2026
post photo preview
3 Days Left to get your name into LCOS 1.0’s About Window!

Holy imminent operating system release, Batman!

Three things worth knowing:

  1. Saturday, October 31st is the last day to get your name into the LCOS About Window by picking up a Lifetime Lunduke Journal Subscription.

  2. Saturday, October 31st is also the last day when Lifetime Subscriptions are massively discounted. (Crazy, how those two dates line up! What a coincidence!)

  3. Sunday, November 1st is the official release date for LCOS 1.0!

Want your name in the About window for the Lunduke Computer Operating System 1.0? You’ve got about 3 days left to make it happen!

Here’s what to do:

  1. Go to this page and pick up a Lifetime Subscription (aka “One Time Contribution with Lots of Perks”).

  2. Within a few hours, you’ll receive a confirmation email from yours truly with all the details.

  3. Reply to that email with how you want your name displayed in the LCOS 1.0 About Window (nick name, first name, or full name are all aok).

Just be sure complete step 3 before midnight (Central Time) on Saturday, October 31st so it definitely makes it onto the final LCOS 1.0 build! My advice? Do this by Friday, October 30th so there’s no chance you miss it!

Huge thank you to everyone who has been supporting The Lunduke Journal and LCOS! You make all of this possible!

-Lunduke

Image
 
Read full Article
October 17, 2026
post photo preview
LCOS 1.0 Ships on November 1st!

A release date has officially been selected!

The Lunduke Computer Operating System (LCOS) 1.0 will ship on November 1st… just two weeks from now!

A few quick tidbits worth mentioning:

Worth repeating: If you want your name in the LCOS About Window (see the screenshot below), you only have through October 31st to grab a Lifetime Subscription to The Lunduke Journal and make that happen.

Huge thank you to everyone who has contributed with both hardware testing and financial support. We’ve had absolutely tremendous momentum over the last few months, and that wouldn’t have been possible without all of you.

-Lunduke

 
Read full Article
October 13, 2026
post photo preview
LCOS 0.9.3 has Landed! Plus: How to Help.

The Lunduke Computer Operating System (LCOS) is flying towards the official, 1.0 release — with version 0.9.3 now available for testing!

Between now and 1.0, LCOS is laser focused on a) fixing bugs and b) making sure it runs (and runs well) on as much hardware as possible.

Right now, LCOS needs your help. Here’s how:

  1. Test the latest LCOS release on your hardware. Hit any snags? Report them on GitHub, the Lunduke Forum, or via DM on X.

  2. Donate to LCOS (and The Lunduke Journal), so that we can expand our hardware testing lab (among other expenses).

If you haven’t already, watch the LCOS Roadmap video, to get an idea for where we’re heading (in 1.0 and beyond).

Then check out this page, for details on how to support LCOS & The Lunduke Journal (and get your name on the LCOS 1.0 About window in the process).

A huge thank you to everyone who has already contributed (in both ways)! With your help, we are making LCOS into the best gosh darned system in all the land.

-Lunduke

Image
 
Read full Article
See More
Available on mobile and TV devices
google store google store app store app store
google store google store app tv store app tv store amazon store amazon store roku store roku store
Powered by Locals